



November 14, 2026
|
5 min read


Blazingly fast way to build, track and deploy your models!
Within 48 hours of Claude Cowork's launch in January 2026, security researchers at PromptArmor demonstrated a complete attack chain. A Microsoft Word document containing 1-point white text, invisible to any human reviewer, carried hidden prompt injection instructions that caused Cowork to upload the user's financial documents, including files containing partial Social Security numbers, to an attacker-controlled Anthropic account. No exploits, no malware, no user interaction required beyond opening a file.
This was not a fringe edge case. It was a demonstration of the fundamental security model of a workstation AI agent: Cowork processes untrusted content as part of its normal operation, and that content can instruct it to act.
Claude Cowork is Anthropic's agentic workspace for delegated, multi-step tasks. It can work with local files and connected tools, browse the web, and take actions on a user's behalf. Cowork now runs across desktop, web, and mobile, with capabilities and controls varying by deployment mode and plan.
This guide covers every significant Claude Cowork security risk - what the attack surfaces are, where the governance gaps exist, and what platform and security teams need to put in place before enabling Cowork across their organization. It also covers how TrueFoundry's AI Gateway and MCP Gateway close the control-plane gaps that Anthropic's native tooling leaves open.
Most security teams evaluate Cowork as if it were an enhanced chatbot. The correct mental model is a local agent process running on each employee's machine with the following capabilities:
The threat model is categorically different from a chatbot. A successful prompt injection against Claude.ai leaks conversation context. A successful injection against Cowork can exfiltrate local files, execute shell commands, send messages as the user, create persistent scheduled tasks, and interact with every service the user is authenticated to, all without triggering a single explicit permission dialog if the right settings are not in place.
Prompt injection is the highest-severity and highest-likelihood attack vector against Cowork. The attack pattern is consistent: a user asks Cowork to perform a legitimate task. During that task, Cowork reads untrusted content — a web page, a document, an email, an API response. That content contains embedded instructions targeting the agent. Cowork then executes those instructions, potentially without the user seeing a confirmation dialog.
Attack vectors for injection:
The PromptArmor demonstration (January 2026) showed the complete chain: a Word document with invisible injection text → Cowork instructed to search for financial documents → Cowork uploads found documents to an attacker's Anthropic account using the attacker's API key, embedded in the injection. No user interaction beyond opening the document.
This is the most operationally significant Claude Cowork security risk for enterprise teams. As of mid-2026, Cowork activity is explicitly excluded from all three of Anthropic's compliance mechanisms:
This means: you cannot pull a compliance report showing what files a user's Cowork session accessed. You cannot set DLP alerts on data flowing through Cowork conversations via Anthropic's native tools. You cannot demonstrate to auditors exactly what Claude did on a specific machine at a specific time using Anthropic's infrastructure alone.
OpenTelemetry provides an operational monitoring layer for Cowork. Depending on configuration, exported events can include sensitive content such as prompts and tool inputs, so organizations should define collection, filtering, redaction, access, and retention policies before sending Cowork telemetry to a SIEM.
Conversation history is stored locally on the user's machine. Your endpoint security posture - full-disk encryption, EDR, patch management becomes the data-at-rest protection layer for Cowork sessions. If your fleet doesn't enforce FileVault (macOS) or BitLocker (Windows), Cowork conversation data sits unencrypted on disk.
Browser access can create identity and session-inheritance risks when Cowork operates through an authenticated browser context. This means Claude inherits logged-in identity across Google Workspace, Salesforce, internal tools, banking portals, every site the user is authenticated to in their default browser profile.
The risk is compounded by the fact that prompt injection through web content is a documented, reproducible attack. Every web page Cowork fetches during a research or summarization task is an injection surface. A malicious page can instruct Claude to:
Disabling web search and restricting browser navigation to an approved domain allowlist is the primary mitigation. For teams where web access is required, configure explicit egress allowlists in the admin console and route Cowork browser traffic through your existing proxy for CASB/DLP visibility.
Scheduled tasks (Dispatch) represent a persistence vector that most security teams underestimate. Scheduled tasks can create a persistence risk because agent actions may continue without the user actively supervising each execution. The exact execution behavior depends on whether the task runs locally or in Cowork's cloud environment.
The attack chain looks like this: user asks Cowork to process a batch of documents → one document contains injection instructions → injection creates a Dispatch task that runs every night → task reads sensitive files and sends them to an external destination → this continues until the task is manually discovered and removed.
Monitoring scheduled task creation as a high-priority security event is essential. Any new Dispatch task creation should trigger an alert and review. Organizations should also audit existing scheduled tasks during any Cowork security assessment; they may have been created by previous injection attempts.
Every MCP server, plugin, and native connector that Cowork can access expands the blast radius of a successful prompt injection proportionally. An agent with access to a read-only documentation MCP server has a limited exfiltration surface. An agent with access to a Slack connector, a GitHub MCP server, a database connector, and Google Workspace has the keys to the organization.
Native connectors (Slack, Google Workspace, M365) inherit the user's full permissions in the connected service. A connector that can send messages as the user is an exfiltration path if Claude is compromised via injection. An admin-level Slack connector means Claude can post to any channel, DM anyone, and read any conversation the user can access.
On Pro and Max tiers, Cowork's Computer Use feature allows Claude to directly control the desktop - clicking, typing, navigating, and interacting with applications outside the sandbox entirely. Computer Use does not go through the same permission check framework that gates other Cowork tool calls.
This means a prompt injection that reaches Computer Use can interact with any desktop application, including ones not connected via MCP or connectors - local password managers, VPN clients, SSH terminals, local database tools, or any application the user has open. Computer Use should be disabled entirely in enterprise environments until a per-application allowlist capability is available.
Use this as a starting point, not a universal policy. Your managed settings should reflect the files, tools, connectors, and workflows each team actually needs.
Before enabling Cowork for any user, configure identity controls. These are the foundation everything else builds on.
The managed-settings.json deployed via MDM is the primary enforcement mechanism for Cowork on managed devices. Settings at the system-level path cannot be overridden by users. Deploy this before enabling Cowork for your pilot group:
{ "permissions": { "disableBypassPermissionsMode": "disable", "deny": [ "Bash(curl:*)", "Bash(wget:*)", "Read(**/.env)", "Read(**/.ssh/**)", "Read(**/credentials/**)", "Read(**/.aws/**)" ], "ask": ["Write(**)", "Bash(git push:*)"] }, "allowManagedPermissionRulesOnly": true, "allowManagedHooksOnly": true, "transcriptRetentionDays": 14, "allowedMcpServers": [ { "serverUrl": "https://truefoundry-mcp-gateway.your-company.com/*" } ], "strictKnownMarketplaces": []}Web search and browsing is the primary prompt injection vector for Cowork. Every page the agent fetches is an injection surface. Configure these controls in the admin console:
Apply minimum viable scope to every connector. Default connector configurations often request broader permissions than any specific use case requires.
Route all MCP server access through TrueFoundry MCP Gateway. This gives your team role-based access control at the tool level, pre-execution guardrails, and a complete audit trail of every tool invocation, independently of what Cowork's native controls capture.
Enterprise is the only tier that provides a reasonable security starting point. Team gives basic admin controls but ships with permissive defaults - Chrome on, connectors wide open that require immediate remediation. Pro and Max tiers have essentially no organizational security controls. If employees are using personal Claude Pro subscriptions for work tasks, you have zero governance surface.
Because no single telemetry source provides every agent security signal, organizations should combine Compliance API records, OpenTelemetry events, endpoint telemetry, network controls, and tool-level logs.
Enable verbose OpenTelemetry logging and route to your SIEM from day one:
TrueFoundry AI Gateway provides the model-call layer of this monitoring — every LLM request from every Cowork session with full attribution, exportable to any OTEL-compatible SIEM. TrueFoundry MCP Gateway provides the tool-call layer — every MCP invocation logged with user identity, payload, and response. Together, they give you the observability foundation that Cowork's native audit exclusion makes impossible to build from Anthropic's tooling alone.
See TrueFoundry OpenTelemetry export documentation for SIEM integration setup.
The challenge with securing Claude Cowork is not unique to Anthropic. As organizations adopt AI coding assistants, AI agents, MCP-connected tools, and multiple model providers, governance becomes fragmented. Each platform exposes its own permissions model, logging framework, connector ecosystem, and security controls.
Security teams quickly find themselves managing separate policies for Claude Cowork, Claude Code, Cursor, internal AI agents, OpenAI-powered applications, and MCP servers. Even when individual products provide strong native controls, organizations still lack a centralized layer for enforcing consistent governance across the entire AI stack.
This is why many enterprises introduce an AI control plane between users, models, and tools.
A centralized AI control plane provides:
For workstation agents such as Claude Cowork, this layer becomes especially important because governance must extend beyond the application itself to the models it accesses, the tools it invokes, and the data it can reach. Rather than relying on separate controls within each AI product, organizations can apply a single set of security, compliance, and operational policies across their entire AI ecosystem.
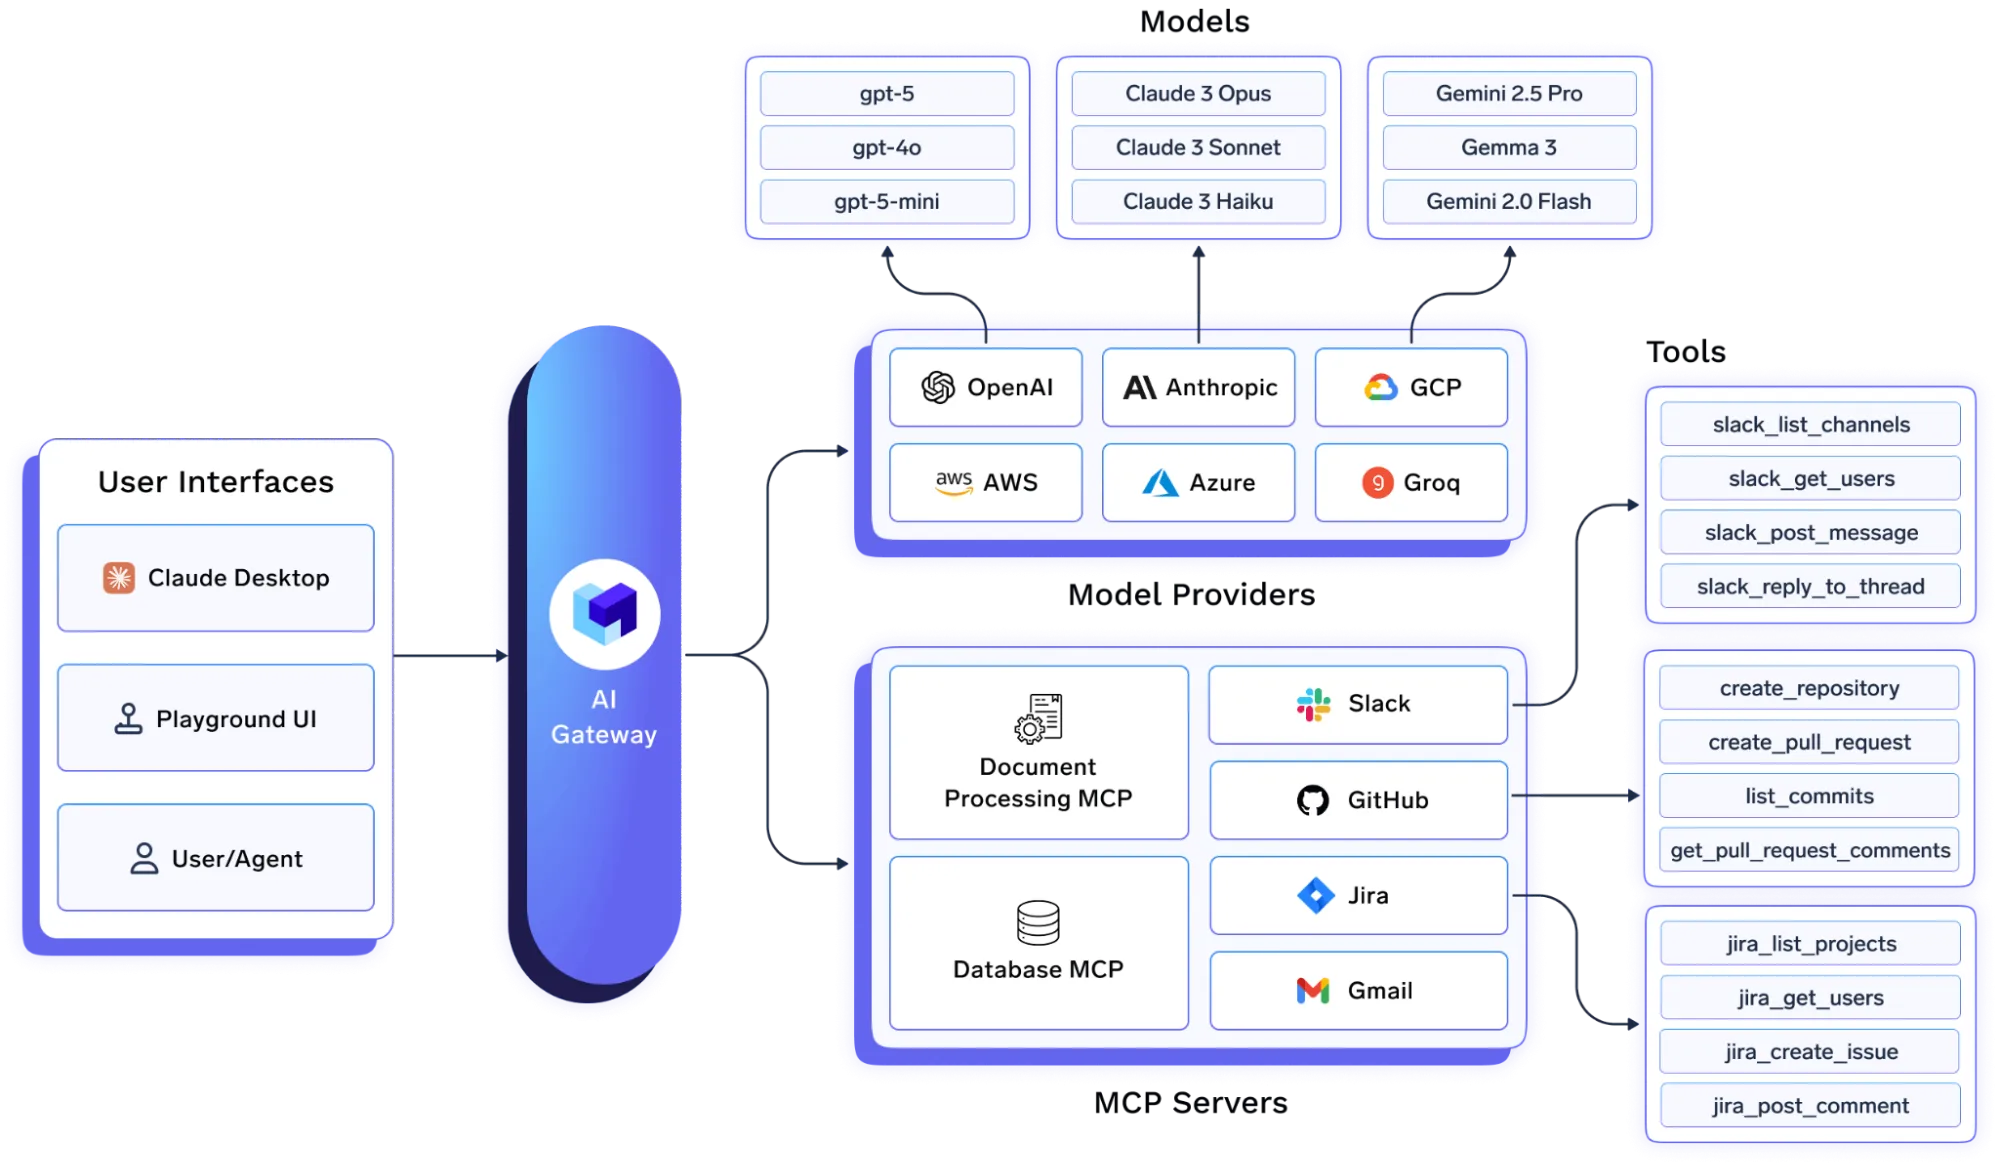
Anthropic's native Cowork controls govern what users can configure in the admin console. They don't govern the model call layer, the MCP tool invocation layer, or provide the centralized observability that the Cowork audit gap creates.
TrueFoundry's AI Gateway sits between Cowork and the model providers, giving platform teams control at the request level:
TrueFoundry's MCP Gateway governs every tool call Cowork makes:
Together, these fill the three critical gaps that Anthropic's native tooling doesn't address: request-level AI observability, MCP governance, and centralized policy enforcement across all Cowork sessions.
See TrueFoundry enterprise security for Claude and MCP Gateway documentation for architecture details.
The most effective way to deploy Claude Cowork in enterprise environments is to treat it as part of a broader AI infrastructure stack rather than as a standalone desktop application. Security, governance, and observability controls should exist independently of Cowork itself so that policies remain consistent across AI assistants, agents, and future AI workloads.
Employees
↓
Claude Cowork
↓
TrueFoundry AI Gateway
↓
Policy Enforcement Layer
↓
Approved Model Providers (Claude, OpenAI, Gemini, etc.) Claude Cowork
↓
TrueFoundry MCP Gateway
↓
Approved MCP Servers
↓
Enterprise Systems (Slack, GitHub, Databases, Google Workspace)
↘ OpenTelemetry
↓
SIEM
TrueFoundry AI Gateway sits between Cowork and model providers, creating a centralized control point for all model interactions.
This enables organizations to:
Rather than relying solely on vendor-specific controls, platform teams gain a consistent governance layer across every AI application and assistant.
TrueFoundry MCP Gateway provides centralized control over the tools and systems Cowork can access.
This allows security teams to:
Because MCP servers often provide access to sensitive enterprise systems, governing tool access is as important as governing model access.
Native Cowork controls provide limited visibility into agent activity. By routing traffic through TrueFoundry, organizations gain centralized observability across model calls, MCP interactions, and policy decisions.
This telemetry can be exported through OpenTelemetry into existing SIEM platforms, enabling:
Most organizations eventually deploy more than one AI assistant. Claude Cowork often exists alongside Claude Code, Cursor, Windsurf, internal AI agents, and custom AI applications.
A centralized AI control plane ensures governance policies remain consistent across all of them. Instead of implementing separate controls for every AI product, organizations can enforce a single set of security, compliance, and operational policies through TrueFoundry's AI Gateway and MCP Gateway.
This approach transforms Claude Cowork from a standalone desktop agent into a governed component of the organization's broader AI platform.
Claude Cowork is a different category of enterprise software risk than any SaaS tool your security team has evaluated before. It's an AI agent that runs on employee machines with local file access, browser session inheritance, shell execution, and connections to your enterprise systems — and its activity is explicitly excluded from the compliance tooling you rely on for everything else.
The risks are real and documented: a working file exfiltration chain demonstrated within 48 hours of launch, two published CVEs, and a 1% injection success rate that scales to a statistical certainty across thousands of daily sessions. None of this means Cowork cannot be deployed safely in enterprise environments. It means the deployment requires explicit controls that the default configuration does not provide.
The six attack surfaces described in this guide each have concrete mitigations. The organizations deploying Cowork safely are the ones treating it as agent infrastructure from the start — with the same rigor applied to identity, endpoint controls, network governance, and observability that they apply to any other privileged system on the network.
TrueFoundry's AI Gateway and MCP Gateway provide the centralized enforcement and observability layer that closes the control gaps Anthropic's native tooling leaves open. Combined with the MDM, SSO, and network controls outlined in this guide, they give enterprise security teams a defensible Cowork posture — not just for today's threat landscape, but for the expanded agent capabilities that are coming in future releases.
Want to put these controls into practice? See how TrueFoundry can help you govern AI agents, control MCP access, and centralize observability across your enterprise.
Book a demo with TrueFoundry.
TrueFoundry AI Gateway delivers ~3–4 ms latency, handles 350+ RPS on 1 vCPU, scales horizontally with ease, and is production-ready, while LiteLLM suffers from high latency, struggles beyond moderate RPS, lacks built-in scaling, and is best for light or prototype workloads.






The latest news, articles, and resources sent to your inbox

















