Blank white background with no objects or features visible.

Hello, EMEA! TrueFoundry is growing our footprint across Europe, the Middle East, and Africa. Read more. →

Best AI Agent Identity Tools: Top 5 for Autonomous Access

By Ashish Dubey

Updated: November 9, 2026

Published: November 3, 2026

The best AI agent identity tools give every autonomous agent its own verifiable identity, authenticate it on each request, and authorize what it can do under least-privilege policy — with delegation, lifecycle controls and audit. They fall into two complementary groups: identity-and-enforcement platforms that issue and enforce agent identity in the request path, and non-human-identity (NHI) security tools that discover and manage the posture of agent identities.

In one line: these are the platforms that replace shared API keys with governed, per-agent identity for agentic IAM.

The top 5 at a glance

ToolTypeDeploymentBest for
TrueFoundryAgent identity + enforcement (AI/MCP gateway)SaaS, VPC, on-prem, air-gappedOne control plane for agent identity, models and MCP
OktaIdentity provider extending to NHI/agentsSaaSOrgs standardized on Okta extending IdP governance to agents
Microsoft Entra Agent IDAgent identities in the Entra directorySaaS (Microsoft cloud)Microsoft/Entra-centric estates (Copilot, Foundry)
Astrix SecurityNon-human identity security postureSaaSDiscovering and securing NHI/agent risk and lifecycle
Oasis SecurityNon-human identity managementSaaSCentralizing NHI/agent access governance across cloud

How to read this list: if you need to enforce identity in the request path (authenticate the agent and authorize each action before it reaches a tool or model), you want an identity-and-enforcement platform. If you need to discover and secure the sprawl of non-human identities you already have, you want an NHI-security tool. Many enterprises use one of each.

1. TrueFoundry

TrueFoundry is an enterprise AI gateway and control plane that treats every agent as a first-class identity and enforces it in the request path. Each agent is registered with its own identity, authenticated on every call, and authorized against least-privilege policy — with on-behalf-of delegation, an MCP registry, SSO/SCIM and full audit — deployable as SaaS, in your VPC, on-prem or fully air-gapped.

What sets it apart in this list is scope: it governs agent identity alongside the models agents call and the MCP servers and tools they reach, from one plane. For teams that want identity, authorization and model/MCP governance in a single enforceable choke point, it is the most complete option.

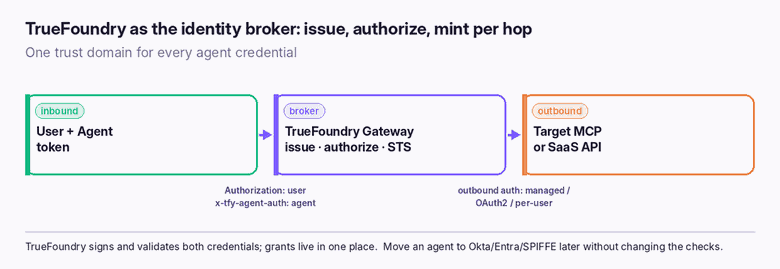
Mechanically, every request carries the user’s token plus the agent’s TrueFoundry-signed token (Authorization + x-tfy-agent-authorization); the gateway resolves the (user, agent) pair, enforces RBAC plus optional Cedar policy, and performs RFC 8693 on-behalf-of delegation that can only narrow access down the chain. Agents are provisioned, certified, drift-monitored and killed from the registry — and outbound credentials to each tool stay in the gateway, never in the agent

TrueFoundry as the identity broker: both the user and agent credentials validated, authorized and re-minted per hop at the gateway.

Top Features:

  • Per-agent identity with authentication and least-privilege authorization enforced at the gateway.
  • On-behalf-of delegation and collaborator-based scoping across agent-to-agent chains.
  • MCP registry and policy on which agents reach which MCP servers and tools.
  • SSO, RBAC/SCIM, full audit, and SOC 2 — deployable SaaS, VPC, on-prem or air-gapped.

Best for: enterprises that want one control plane governing agent identity, authorization, models and MCP. See the agent governance key concepts and the identity-broker pattern.

Give every agent a governed identity and least-privilege access in the request path.

2. Okta

Okta, a leader in workforce and customer identity, has extended its Identity Security Fabric toward non-human and agent identities — issuing identities to agents, governing their access, and bringing agent authentication into the same IdP enterprises already use for people. For organizations standardized on Okta, extending that governance to agents is a natural path.

  • Auth for GenAI: secure, user-consented API/tool access for AI agents, with a token vault and fine-grained authorization.
  • Cross App Access, built on the identity-assertion authorization-grant (ID-JAG) standard, for governed app-to-app and agent access.
  • Non-human identity governance and threat protection extended from its workforce-identity platform.

Best for: Okta-centric enterprises that want to extend their existing identity provider to cover agents. (TrueFoundry integrates with Okta for agent identity — see TrueFoundry with Okta.)

3. Microsoft Entra Agent ID

Microsoft Entra Agent ID brings AI agents into the Entra directory as first-class identities, so agents can be governed with the same directory, conditional-access and lifecycle tooling Microsoft shops use for users and workloads. It is the obvious fit for estates built on Microsoft — especially agents from Copilot Studio and Microsoft Foundry.

  • Agents built in Copilot Studio and Azure AI Foundry automatically receive identities in the Entra directory.
  • Governed with familiar Entra tooling — Conditional Access, access reviews and lifecycle — and visible in the Entra admin center.
  • Tight integration with the Microsoft agent ecosystem.

Best for: Microsoft/Entra-centric organizations. (TrueFoundry governs Entra-issued agents reaching MCP servers — relevant when agents span beyond the Microsoft estate.)

Want agent identity enforced in the request path, not just monitored?

4. Astrix Security

Astrix Security is a non-human identity security platform. Rather than sitting in the request path, it discovers the NHIs and AI agents already in your environment, flags over-privilege and anomalies, and helps manage their lifecycle — the posture-and-risk side of agent identity.

  • Discovery and inventory of non-human identities and AI agents across connected systems.
  • Posture management, over-privilege detection and identity threat detection and response (ITDR) for NHIs.
  • Lifecycle management and remediation, including offboarding of stale or risky identities.

Best for: security teams that need visibility into, and control over, NHI/agent risk across existing systems. Pairs well with an enforcement platform.

5. Oasis Security

Oasis Security is a non-human identity management platform built for the scale of service accounts, workloads and now agentic access. It centralizes discovery, governance and lifecycle for non-human identities, with a growing focus on agentic access management.

  • Centralized discovery and ownership context for non-human identities.
  • Lifecycle automation — provisioning, rotation and decommissioning — with least-privilege controls.
  • Purpose-built for non-human and agentic access management at scale.

Best for: enterprises wanting a dedicated plane to govern the full population of non-human identities, agents included.

See how TrueFoundry governs agent identity, models and MCP from one plane.

How to choose an AI agent identity tool

  • Need identity enforced in the request path (authN + least-privilege authZ before a tool/model is reached): TrueFoundry.
  • Already standardized on Okta or Microsoft Entra: extend your IdP with Okta or Entra Agent ID — and front agent-to-tool traffic with a gateway for enforcement.
  • Need to discover and secure existing NHI/agent sprawl: Astrix or Oasis.

The honest answer for most enterprises: pair an enforcement control plane (so agents authenticate and are authorized per action) with an NHI-security tool (so you can see and clean up what you already have). They solve different halves of agentic IAM.

Related reading

Try now.

One gateway for all your models, MCP servers, and agents. No credit card needed.

Start free
Table of Contents

One Gateway for Every LLM, Agent and MCP Server

Book a 30-min with our AI expert

Book a Demo

The fastest way to build, govern and scale your AI

Book Demo
Summarize with
ChatGPT logo by OpenAI
Perplexity AI logo
Blurry red snowflake on white background, symmetrical frosty design with soft edges and abstract shape.

Discover More

No items found.
November 14, 2026
|
5 min read

Claude Managed Agents vs LangChain Deep Agents: Which Agent Harness Should You Choose?

TrueForge
November 13, 2026
|
5 min read

Claude Managed Agents vs TrueForge: Which Agent Harness Should Enterprise Teams Run in 2026

TrueForge
 What is an LLM Gateway
November 13, 2026
|
5 min read

What Is an LLM Gateway? How It Works, What to Look For, and When You Need One

Engineering and Product
November 13, 2026
|
5 min read

How to Host Helm Charts on GitHub Pages and Publish Them on Artifact Hub (2026 Guide)

Engineering and Product
No items found.

Recent Blogs

Black left pointing arrow symbol on white background, directional indicator.

Frequently asked questions

What are the top 10 IAM tools?

Some leading identity and access management tools for AI agents include TrueFoundry, Okta, Microsoft Entra Agent ID, Astrix Security, Oasis Security, Aembit, SlashID, P0 Security, Corsha, and SailPoint. These platforms offer capabilities such as agent authentication, authorization, identity discovery, credential management, and lifecycle governance to help enterprises secure autonomous access.

What are examples of agent tools?

Examples of AI agent identity tools include TrueFoundry, Okta, Microsoft Entra Agent ID, Astrix Security, and Oasis Security. TrueFoundry provides agent identity and runtime access enforcement, while Okta and Microsoft Entra extend existing identity management capabilities to agents. Astrix and Oasis focus on discovering, governing, and securing non-human identities across enterprise environments.

What are the best identity access management tools?

The leading identity and access management tools for AI agents include TrueFoundry, Okta, Microsoft Entra Agent ID, Astrix Security, and Oasis Security. These platforms help enterprises manage agent identities, authenticate requests, enforce least-privilege permissions, and monitor access. The best solution depends on existing infrastructure and whether the priority is identity enforcement or non-human identity governance.

What is the best agent platform?

TrueFoundry is a strong choice for enterprises seeking a unified AI agent identity and enforcement platform. It provides per-agent authentication, least-privilege authorization, on-behalf-of delegation, MCP governance, and audit capabilities through a centralized control plane. Organizations can deploy it through SaaS, VPC, on-premises, or air-gapped environments.

What are AI agent identity tools?

AI agent identity tools give autonomous agents their own verifiable identities and govern their access — authenticating each agent, authorizing its actions under least privilege, and auditing what it does. They replace shared API keys and borrowed human credentials with per-agent, governable identity.

What is the best AI agent identity tool?

It depends on whether you need enforcement or posture. For enforcing agent identity and least-privilege access in the request path — alongside model and MCP governance — TrueFoundry is the most complete. For extending an existing identity provider, Okta or Microsoft Entra Agent ID; for securing existing NHI sprawl, Astrix or Oasis.

Do AI agents need a different identity solution than humans?

Yes. Agents are autonomous, ephemeral and act on others’ behalf, so human-shaped IAM leaves gaps around attribution, least privilege, delegation and lifecycle. Agent identity tools address those specifically, treating each agent as a first-class non-human identity.

What is the difference between an agent identity platform and an NHI security tool?

An identity-and-enforcement platform issues and enforces agent identity in the request path (authentication and authorization before an action runs). An NHI-security tool discovers and secures the non-human identities you already have, focusing on posture, over-privilege and lifecycle. Many enterprises use both.

Take a quick product tour
Start Product Tour
Product Tour